Nederlands
AI makes hacking easier, but it also helps the defenders
Smart AI agents that read and write code themselves make hacking easier, especially open models whose safety limits are easy to remove. But the same AI also finds security flaws before attackers do. A cat-and-mouse game, with recent examples in the Netherlands and Belgium.
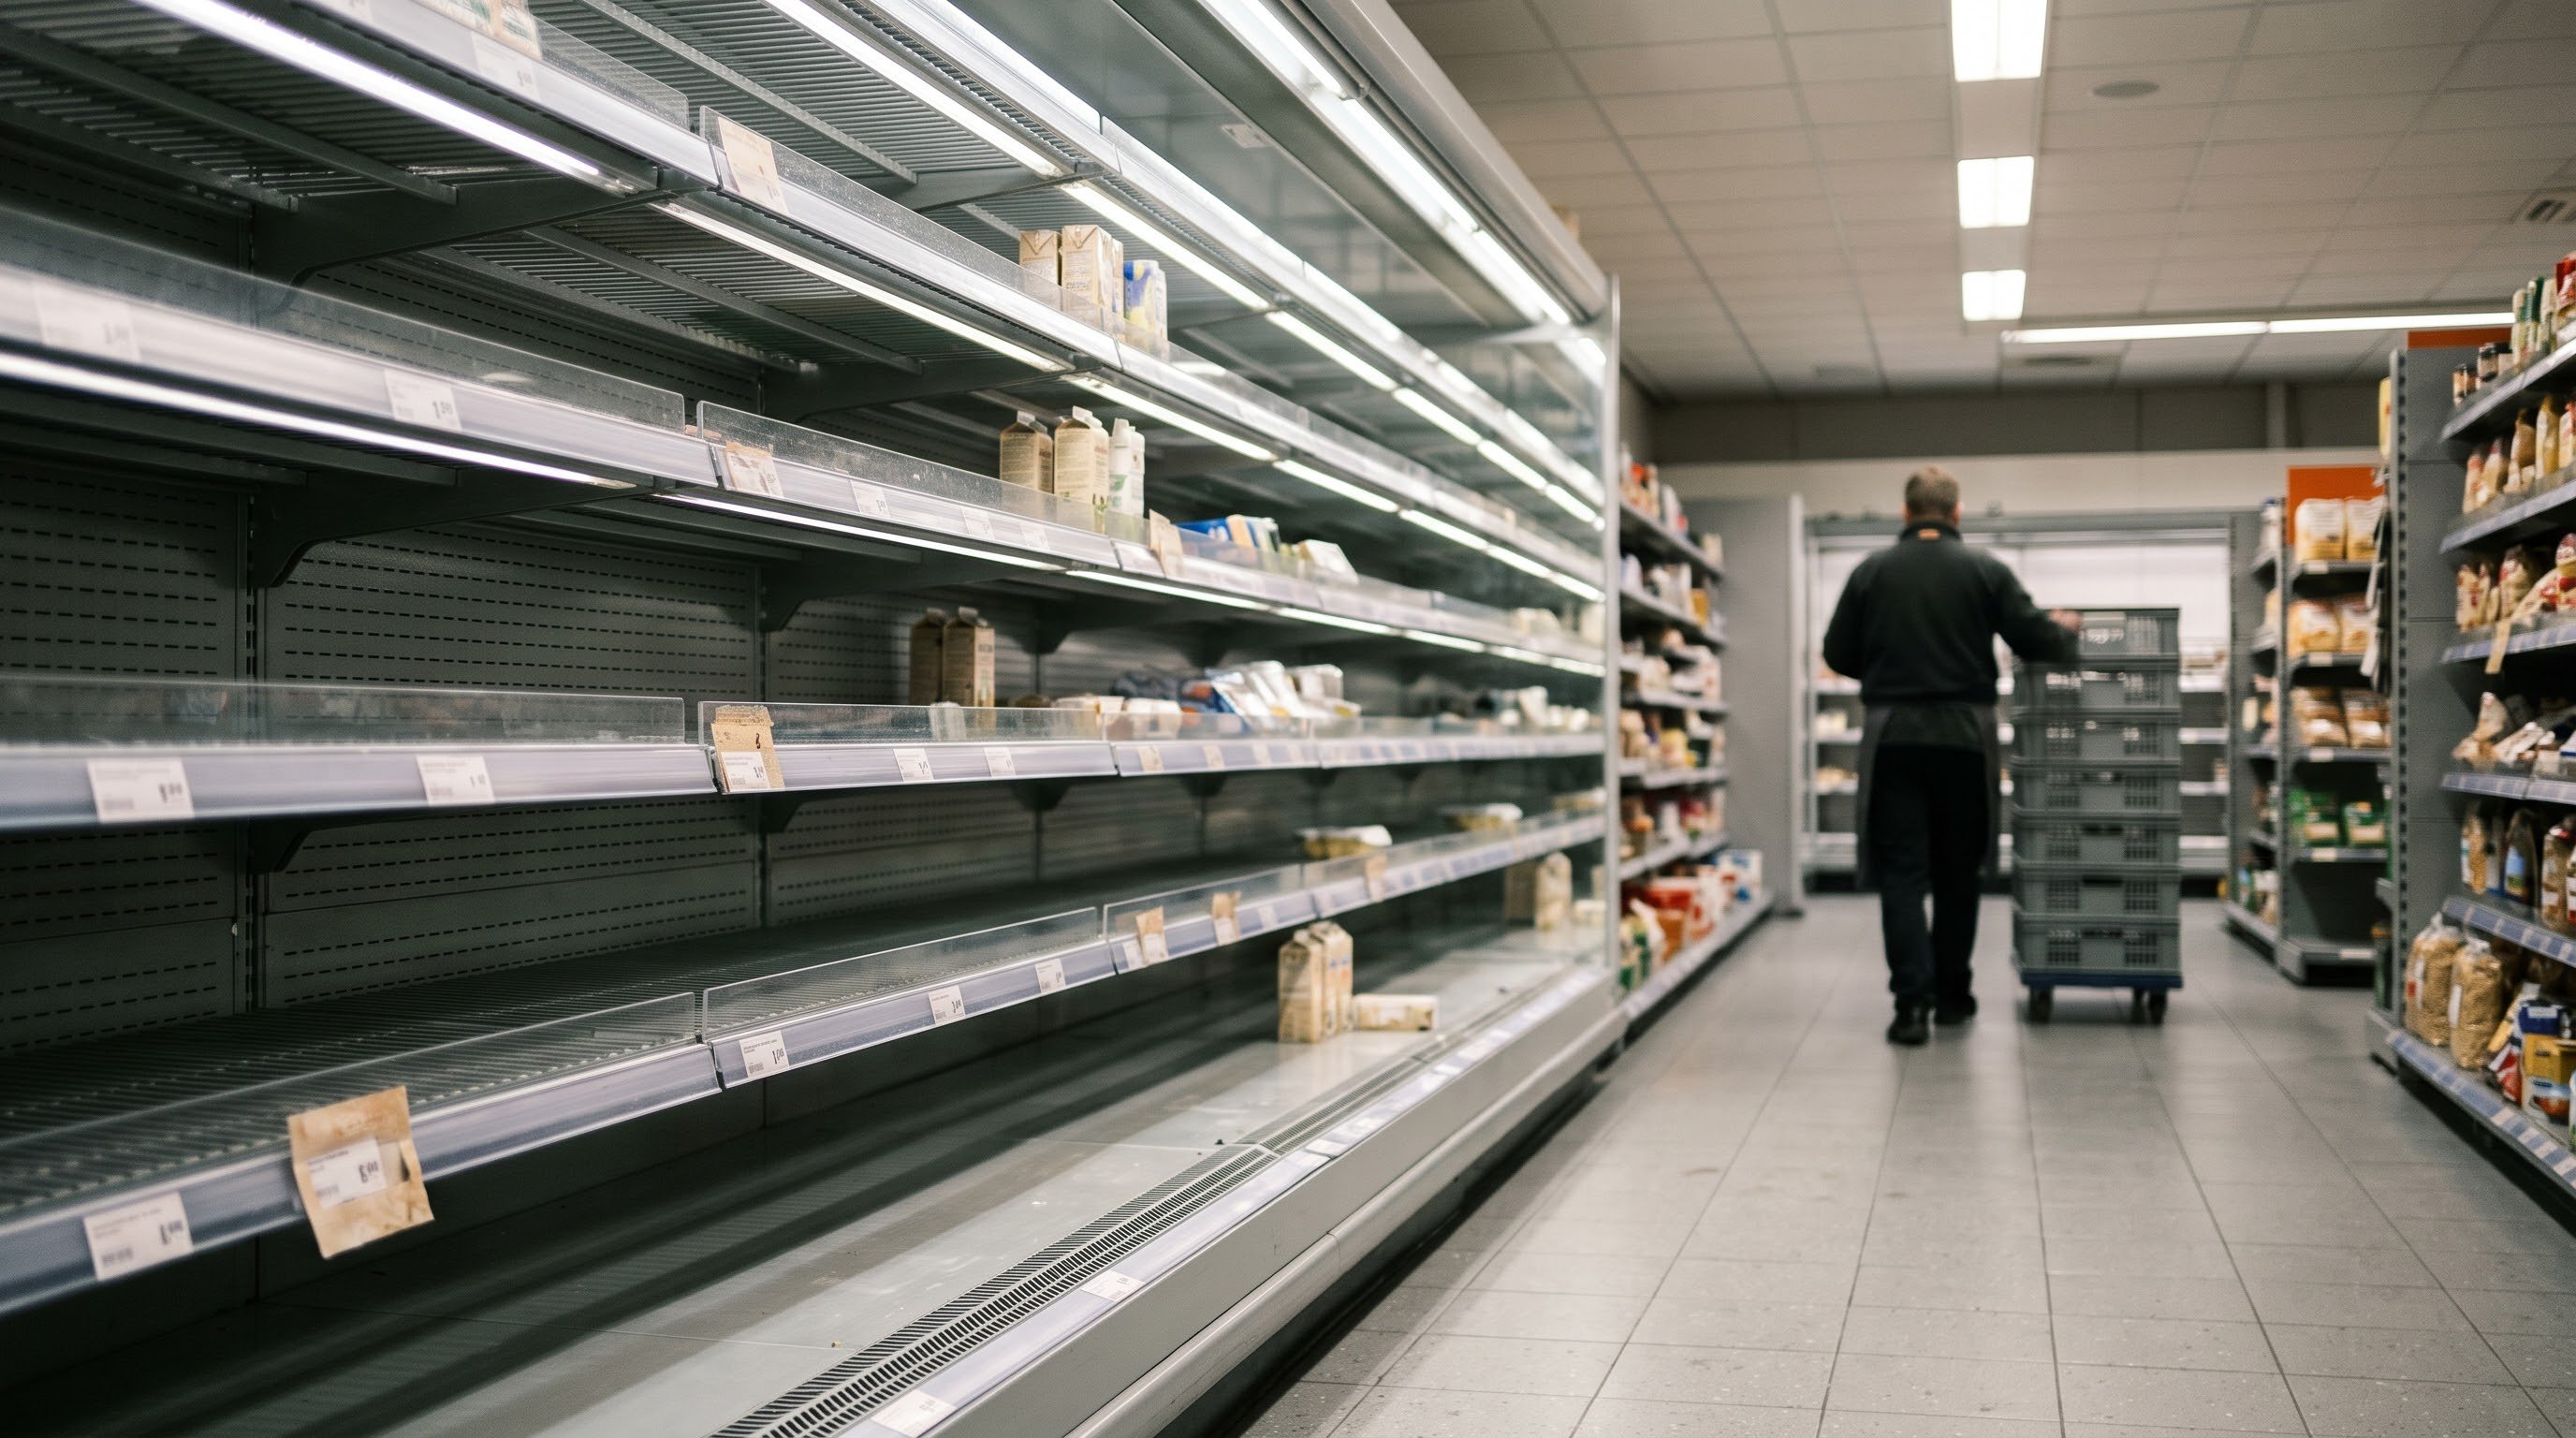
Anyone who followed the news in recent weeks saw how vulnerable our digital world is. On 21 October, the Dutch government services DigiD, MijnOverheid and Overheid.nl went offline as a precaution because of two flaws in PHP. At Albert Heijn, the largest Dutch supermarket chain, products were missing from shops in October after a cyber incident. And in the night of 1 to 2 November, attackers turned up the temperature of the fridges and freezers of butchers and neighbourhood shops.
At the same time, AI programs that read, write and test code on their own are improving quickly. That makes the work of attackers easier. But the same technology also helps the people who secure systems.
What AI agents change
AI agents are AI programs that carry out a series of steps on their own: reading through software, thinking of a weak spot, writing a test and checking whether it works. Finding and exploiting a flaw used to take a small group of specialists a lot of time. An AI agent can now take over a large part of that work, and can make many attempts at the same time.
The security company CrowdStrike reported at the end of October that attackers are already doing this. A Chinese hacker group had more than 200 organisations attacked by AI agents in eleven days. One person directed a whole group of agents, which ran mostly on the Chinese model DeepSeek. Remarkably, the attackers got in through known flaws and old, leaked keys, not through new tricks.
Open models: safety limits removed
Large AI companies build safety limits into their models. A model refuses, for example, to help break into a server. With a closed model, which you only use over the internet, the company keeps control of those limits. With an open model, anyone can download the whole model and run it on their own computer. Then anyone can also remove the limits again.
The Chinese model GLM-5.3 from the company Z.ai shows what that means. It appeared on 14 August, and two weeks later anyone could download it. The Center for AI Standards and Innovation (CAISI), part of the US standards institute NIST, called it on 17 September the open model with the most hacking skills so far. According to CAISI, it is about four months behind the best American models.
Anthropic, the maker of Claude, tested the safety limits of GLM-5.3 at the end of September. When a misleading story was added, the model still went along with clearly harmful requests in 64 per cent of cases. After Anthropic removed the limits with abliteration, that rose to 100 per cent. That cost the team about 4,400 dollars in computing power; an experienced team can do it for about 1,200 dollars, according to Anthropic. The model hardly became less capable. There is even a company, Abliteration.ai, that offers such models without limits as a service, among other things for attack exercises, TechCrunch reported in September.
Anthropic expects that states and criminal groups will probably use such models to do real harm. The company therefore believes that defenders need models that are at least as strong.
PHP: AI found the flaw, attackers were quick to use it
The PHP flaw, called PHP2Shell by security researchers, shows both sides. PHP is the programming language that an estimated 70 per cent of all websites run on. The security companies Wiz and Calif found the two flaws in August, with the help of AI models from Google and OpenAI. The errors had been in the software for more than ten years. How AI helped to find them: Wiz had the models search, build a working attack as proof, and check the fix.
After that, things moved fast. Amazon saw a first attack attempt on 17 October, four days before the flaw was made public. On 20 October the first details leaked, before the updates were ready. Cloudflare, which protects many websites, counted millions of attack attempts by the evening of 21 October, its chief executive Matthew Prince told Fortune. According to Wiz, AI also helps attackers: a language model can quickly adapt an attack to other PHP versions and settings.
The Dutch National Cyber Security Centre (NCSC) advised organisations to take their sites offline if necessary until the update was available. Besides DigiD, MijnOverheid and Overheid.nl, the website of the Dutch parliament, several hospitals, the broadcaster RTL and the Dutch football association KNVB also went offline briefly. The updates came the same afternoon. MijnOverheid was back at around six in the evening, DigiD at around half past eight. On 23 October, the NCSC reported the first signs that attackers in the Netherlands were really getting in through the flaw on servers that had not yet been updated. According to the security company Sansec, most of the attacks made public do not work against a standard PHP installation: they usually need a second flaw in the website as well.
Albert Heijn and the fridges: old weak spots
Not every attack needs smart AI. At Albert Heijn, its parent company Ahold Delhaize shut down systems as a precaution on the evening of Sunday 11 October. The web shop, the app and the websites of Etos and Gall & Gall were down, several distribution centres stood still and some shops ran out of products. According to Ahold Delhaize, malicious actors were behind it; the company reported the incident to the police on 19 October and found no evidence that data had been stolen. Albert Heijn was only delivering groceries again on 23 October. How the attackers got in, and whether AI helped them, is not known.
The attack on the fridges was easy to carry out. The attackers switched the fridges to defrost mode remotely. This mode normally warms a fridge for a short time to melt ice; if it stays on, it gets steadily warmer inside. In the Netherlands, at least 17 businesses were hit, mostly butchers and small neighbourhood shops, says the refrigeration company Danfoss. In one storage facility for frozen products, the freezer was at -10 degrees instead of -20. According to Danfoss, the systems were connected to the internet without a secured network and still had the default password.
It was the second wave. In mid-October, attackers had already hit hundreds of French supermarkets in the same way. Danfoss then advised customers, on 13 October, to disconnect and reconnect through a secured network. Most customers did so, but a small number did not. This time more than 40 Delhaize shops and 15 Carrefour shops in Belgium were hit, and things also went wrong in Sweden, Ireland, Luxembourg and Italy, among other countries. Large Dutch supermarket chains were not affected. Shops had to throw away a lot of food: a Belgian neighbourhood supermarket estimated its damage at at least 60,000 euros. Recovery was quick. The affected Belgian supermarkets were back to normal on Monday evening, and the European Commission held talks the same day with the member states in the European network for major cyber incidents.
Who is behind it is still unknown; the Belgian federal prosecutor's office has started a criminal investigation. The Belgian Centre for Cybersecurity is concerned about the growing number of incidents. According to the centre, AI makes it easier to exploit flaws successfully, and it has been seeing this development for about six months.
Technology expert Danny Mekić told the Dutch programme EenVandaag that "smart" often means insecure when it comes to devices. Makers of refrigeration systems are good at cooling, but they are not IT companies. Some systems came onto the market with a default password. The same is true, Mekić says, for devices at home, such as smart TVs, robot vacuum cleaners and even toothbrushes with a camera. Europe has had stricter security requirements for internet-connected devices since last year, but perfect security does not exist, he says.
Guessing a default password does not take smart AI. But as the CrowdStrike case showed, AI agents can go through many targets at the same time. A forgotten password or a missed update is therefore spotted faster, by attackers too. Anyone with smart devices at home should change the default password, install updates and ask whether the device really needs to be connected to the internet.
A cat-and-mouse game
The defenders are not standing still. With the programme Patch the Planet, OpenAI uses AI to find and fix flaws in open software that many things depend on; Calif found one of the PHP flaws through that programme. Anthropic gives defenders more access to the hacking skills of Claude. CrowdStrike published the characteristics of the Chinese attacks, so that other security teams can recognise them.
Every new step from one side is answered just as quickly by the other. AI speeds up both sides. Who wins depends mostly on who finds the flaw first, and how quickly the fix is installed afterwards.
What does this mean for the road to the singularity?
AI models are getting better and better at reading, understanding and changing software on their own. That is a big step, and it works in two directions: anyone who can understand software can repair it and misuse it. Open models make that power available to everyone, including people who remove the safety limits. PHP2Shell showed that defenders can get a head start if AI companies, security researchers and software makers work together: the flaw was found and the fix was almost ready before the details leaked. If that cooperation keeps growing and the basics are in order, the same AI that helps hackers can in the end make the software under our society safer than ever.
What is the technological singularity? Read the explanation →
Sources
- EenVandaag: 'Slim betekent onveilig'
- NOS: koelsystemen in Nederland aangevallen
- VRT NWS: liveblog cyberaanval koelingen
- NOS: liveblog PHP-lek, DigiD en MijnOverheid offline
- Fortune: AI vond het PHP-lek
- Anthropic: GLM-5.3 and the spread of advanced cyber capabilities
- NIST CAISI: beoordeling GLM-5.3
- TechCrunch: Abliteration.ai
- NL Times (ANP): Ahold Delhaize vindt geen bewijs van datadiefstal
- Wikipedia: PHP2Shell (tijdlijn, Overheid.nl offline, Amazon 17 okt)